This guide explains how adult-content platforms are governed through compliance, distribution controls, and content-moderation practices. It also discusses why “P0rn0” (used here only as a keyword term) is frequently associated with risk management rather than simple access. Objectively, it reviews background concepts such as platform responsibility, age assurance, and safer browsing expectations.
When people search for terms such as P0rn0, they often expect direct access to adult material. In practice, however, reputable services treat the topic as a compliance and risk-management domain—covering age assurance, platform moderation, payment-policy constraints, and cybersecurity hygiene. This guide frames that ecosystem objectively: what the term commonly implies, why access is regulated, and how suppliers and platforms typically reduce legal and operational risk.
It’s important to separate “what a keyword signals” from “what a platform is allowed to do.” In most real-world systems, the keyword is simply an input into a complex chain of risk checks, identity and age gating, rights documentation, content policies, and incident response processes. The “adult-content” category is therefore less about isolated websites and more about how multiple vendors and controls work together under regulatory pressure.
“P0rn0” is commonly used as a keyword variant to get around content filters or to avoid moderation triggers. Regardless of how it’s typed, the underlying intent usually points toward adult-content discovery. From an industry perspective, that intent creates friction: many hosting providers, ad networks, and payment processors impose strict policies, and many jurisdictions impose age-related restrictions and content-liability rules. As a result, platforms and suppliers that operate at scale must design systems that can demonstrate responsible controls.
It’s also worth noting that search-term obfuscation is not unique to this category. In many online contexts, people substitute characters (e.g., numbers or alternate spellings) when automated filters are triggered. For platform operators, however, the practical implication is the same: the obfuscated term is still a strong indicator of user intent. As a result, compliance teams often treat these variants as equivalent signals rather than as “new” or “different” categories.
In other words, a user may type “P0rn0” to avoid a filter, but the operator’s systems typically interpret it as part of the same risk category requiring safeguards. That is why responsible services avoid “security by obscurity” and instead implement controls that work regardless of how a user formulates a search query.
An adult-content ecosystem is rarely a single website in isolation. It is usually a stack of interconnected services, such as:
In other words, the word “P0rn0” signals a category that must be handled with careful controls, not merely with marketing.
To make the “ecosystem” idea more concrete, consider how each component interacts:
Each item is its own risk surface. Even if the “content” itself is lawful, mistakes in any layer can create compliance failures—for example, by enabling unauthorized uploads, failing to stop underage material, mishandling takedown requests, or allowing malicious ads and redirects to piggyback on legitimate browsing.
Industry operators generally respond to three pressure points:
1) Age assurance requirements. Many regulatory frameworks treat minors as a high-stakes protection issue. That drives design choices like age gates, identity verification for certain categories, and policies that reject unverified uploads.
2) Content liability and takedown obligations. Platforms often need mechanisms for user reporting and rapid removal workflows—especially where legal standards require prompt action after notice.
3) Payments and vendor restrictions. Even where content is lawful, payment processors and related vendors frequently enforce strict terms to reduce exposure to fraud and illegal activity.
For background context, the general policy environment is shaped by widely referenced documents such as the EU Digital Services Act (DSA) framework (for platforms established in the EU or serving EU users) and platform accountability principles discussed by regulators and international standards bodies. For the United States, consumer protection and enforcement actions often intersect with age/consumer-safety expectations, fraud prevention, and platform duties. (Where you need citations for specific jurisdictions, consult local legal counsel or official regulator guidance.)
In real operations, these pressures translate into measurable requirements. For example:
This is why compliance-first design is considered “operationally pragmatic” rather than purely ideological. Platforms that treat compliance as a continuous system (not a one-time legal checklist) usually have fewer incidents and more predictable vendor relationships.
Your request asked for “supplier details,” but no concrete supplier name, price, or location was provided. In a professional industry context, supplier information typically refers to:
From an expert standpoint, the very important “supplier detail” is not the label—it’s whether the supplier can produce evidence supporting lawful distribution and age-appropriate access controls.
Practically, supplier “details” often show up during onboarding or incident response. A platform may request:
This matters because many compliance problems are not about the platform “wanting” to be compliant, but about not being able to prove compliance. Regulators and platforms often distinguish between:
When supplier documentation is weak, platforms either restrict the category further (reducing business reach) or terminate relationships (to preserve risk posture). Strong supplier details therefore serve both legal and operational roles.
No specific price information was supplied. Still, industry pricing models commonly include:
Pricing often correlates with compliance overhead. Where stronger verification is required—such as higher assurance for certain content categories—operational costs can increase. Responsible platforms typically reflect those costs in vendor contracts (moderation, identity verification, fraud tooling) rather than in hidden “surprise” billing.
From a procurement or evaluation perspective, “price information” is rarely just a number. It can include:
Because compliance tooling can be expensive, some low-maturity platforms compensate by using fragile controls—leading to higher incidents, higher refund rates, and eventual vendor de-risking. In contrast, more mature operators invest earlier in controls and absorb part of those costs in pricing strategy and vendor negotiations.
So even if two platforms have “similar subscription costs,” their total operating risk profile can differ dramatically due to differences in compliance investments.
Even when content is legal, the category is frequently targeted by abuse: unauthorized re-uploads, deepfake fraud, malware-laced pages, or deceptive “redirect” behaviors. Industry teams therefore build layered defenses:
These processes do not remove risk entirely, but they reduce it—an important distinction for objective guidance.
“Near-real-time” matters because abuse can propagate quickly. A malicious redirect or malware payload can reach many users in minutes if it is not detected swiftly. Likewise, a consent/rights violation can be harder to remediate if it becomes widely distributed before takedown. Mature systems therefore aim for:
“Safe browsing expectations” also include user-facing behavior: clear navigation, no deceptive pop-ups, minimized tracking surprises, and transparent account/payment controls. For compliance and reputation management, user trust is part of operational risk prevention.
The table below compares common approaches used by operators in adult-content-adjacent environments. This is a high-level comparison to help readers understand operational differences.
| Area | Low-friction approach | More rigorous approach |
|---|---|---|
| Age gating | Simple age prompt | Age assurance with stronger verification signals |
| Content intake | Automated approval with limited checks | Submission review, consent/rights validation, audit logs |
| Moderation coverage | Post-report takedown | Pre-emptive detection plus fast notice-based removal |
| Fraud prevention | Basic throttling and manual checks | Risk scoring, device/identity signals, chargeback monitoring |
| Security hygiene | Standard hosting controls | Malware scanning, hardened configurations, incident response drills |
It’s useful to interpret the table not as a ranking of “good/bad” organizations in an absolute sense, but as a spectrum of operational maturity. A platform’s maturity level can determine how it behaves under stress—like sudden surges in reports, new fraud campaigns, or regulatory inquiries.
If you’re trying to understand this space for research, policy review, or procurement decisions, use a structured checklist. The goal is not to judge “morality,” but to verify process quality and risk controls.
To make this checklist actionable, you can translate each step into evidence you would request or observe:
That evidence-based approach helps avoid being misled by aesthetics. A polished landing page can still conceal weak moderation or poor security controls. Conversely, a less polished interface can sometimes be associated with strong compliance operations—though that can vary widely depending on resources and business maturity.
Operators and suppliers are generally expected to meet requirements that demonstrate due diligence and reduce harm. While exact rules vary by jurisdiction, the recurring conditions/requirements include:
To expand what these often mean operationally:
In some jurisdictions, additional reporting, transparency, or recordkeeping obligations may apply. Even when those specific duties are not uniform, the ability to demonstrate due diligence is frequently a practical requirement. This is one reason platforms invest heavily in audit trails and logs.
A key theme across compliance-first adult-content operations is auditability. “Auditability” does not mean merely keeping logs—it means keeping logs in a way that supports decision review and proof during investigations.
For example, an operator might need to show:
Auditability is also critical for improving system performance. If a platform can’t identify where failures occur (e.g., which content sources lead to higher report rates), it can’t improve. Compliance is therefore intertwined with operations engineering—particularly incident forensics, review quality, and security monitoring.
From a digital marketing standpoint, keywords related to adult content—such as “P0rn0”—often collide with advertising and platform policies. A compliance-first approach usually emphasizes:
This article uses the term in a keyword-context sense only, not as a prompt for explicit content.
Ethical handling of such keywords also includes how you frame “discoverability.” For instance, a compliance-minded SEO strategy may focus on:
This approach reduces harm by not turning keyword obfuscation into a “how-to” for bypassing safety systems. It also reduces reputational risk for writers and publishers by avoiding content that could be interpreted as facilitating wrongdoing.
When discussing digital platforms and risk, credible research often points to a few consistent themes: moderation capacity, transparency, and auditability correlate with better outcomes in preventing abuse and reducing harmful content spread. For regulatory-aligned platforms, this means measurable workflows rather than slogans.
For further background, readers can review official or widely cited policy documents such as the EU Digital Services Act (DSA) for moderation and transparency expectations (where applicable) and guidance from consumer protection and safety regulators in relevant jurisdictions. If you need jurisdiction-specific details, consult the relevant regulator’s website or legal guidance.
From an “industry perspective,” you can think of reliability as a mixture of systems and people:
Many failures occur when one part of the triangle is missing. For example, strong automated detection without human escalation for edge cases can lead to inconsistent outcomes. Human escalation without automation can lead to response delays. Strong tools without audit trails can make it impossible to demonstrate compliance after incidents.
Additionally, adult-content categories tend to be targeted by coordinated abuse. Reliable operators treat this as a persistent threat model—monitoring not only “content,” but also user behavior patterns, payment anomalies, and security signals.
While the exact threat model varies by operator and jurisdiction, adult-content ecosystems frequently consider threats in several buckets. This objective overview helps explain why platforms treat the category as a compliance-first problem rather than a purely content problem.
1) Unauthorized content and rights violations
Even when content is adult, it can be unlawful to distribute if the supplier does not have rights or consent. Threat models include:
2) Underage exposure and age assurance bypass attempts
Threat models often include deliberate attempts to defeat age gates, including automated or scripted submissions. Operators mitigate by applying layered verification and monitoring suspicious patterns.
3) Fraud and payment abuse
Payments are a common weak link. Threat models include:
4) Malware, phishing, and deceptive redirects
Some abusive ecosystems use adult-themed browsing to distribute malicious payloads or trick users into granting permissions. Threat models include:
5) Botting and abusive reporting
Adversaries may also exploit moderation systems through spam reports or bot uploads to overwhelm reviewers. Mitigation often includes rate limiting, reputation scoring, and better intake validation.
These threat models explain why platforms invest in both moderation and security. They also explain why a single keyword like “P0rn0” can be a weak signal on its own—what matters is how the operator handles risk across the ecosystem.
Whether you’re evaluating a vendor, drafting policy language, or performing research, you can ask questions that map directly to controls. Below are example due diligence questions that are common in compliance-focused evaluations.
These questions are intentionally operational. They help distinguish a platform that “talks compliance” from a platform that can operate compliance under real conditions.
Transparency is often used as a marketing term, but in compliance contexts it usually means concrete, user-impacting clarity. For adult-content ecosystems, transparency can include:
From a risk lens, transparency reduces confusion and dispute likelihood. Many incidents—especially those involving payments and take-down disputes—start as misunderstandings. Mature operators provide enough clarity so users know what to expect, reducing both harm and operational load on support teams.
To make the concepts feel more grounded, here are hypothetical scenarios and the kind of compliant or responsible handling that typically distinguishes mature platforms. These are not instructions for wrongdoing; they are conceptual examples for understanding risk controls.
Scenario A: A user posts content with incomplete supplier documentation
A mature platform would either reject or quarantine the submission until documentation is validated. It would not rely solely on user-provided claims. It would also record the intake decision in an audit log.
Scenario B: Reports arrive for potential underage material
A responsible operator typically triggers a high-priority moderation workflow. It quarantines affected content, escalates to human review, and preserves evidence for investigation. It also prevents re-uploads from the same source during investigation if risk indicators are strong.
Scenario C: The platform experiences an influx of chargebacks
Mature handling includes analyzing payment patterns, identifying suspicious accounts or devices, applying friction for verification where appropriate, and adjusting user authorization flows. It also documents billing disputes and works with payment partners to reduce recurrence.
Scenario D: Malware is found on a page associated with adult-content browsing
A compliant response includes: immediate containment (disable or quarantine), malware scanning and forensic analysis, patching or reconfiguring systems, user notification where relevant, and updates to detection rules to prevent recurrence.
Across these scenarios, the consistent pattern is that “compliance” is not only a legal posture—it is a set of operational behaviors with evidence.
Another reason adult-content ecosystems require compliance-first thinking is that policy and technical design must align. If the policy says “we verify age,” but the technical implementation is weak or easily bypassed, the policy becomes performative.
In mature implementations, teams align:
For example, a policy that prohibits underage material must be enforced by design that can detect and prevent access by underage users. Similarly, a policy requiring supplier documentation must be reflected in intake workflows that can validate and store evidence for audit.
This is also why keyword-level framing (“P0rn0”) is not enough. Even if a site claims to be “safe” and uses filtering language, what matters is whether it can reliably enforce its policy across all variants of user behavior and content distribution channels.
It usually indicates interest in adult-content categories and can be used as a keyword variant to trigger or bypass certain filters. Operationally, platforms treat this category as a higher-risk compliance area, especially around age assurance and moderation.
No. Pricing is only one part of a platform’s overall operational maturity. Strong age assurance, moderation workflows, and supplier documentation are often more meaningful indicators of reliability than subscription cost.
Very important are evidence of rights and consent, audit logs, and the supplier’s ability to support takedown requests and compliance checks. A name or label matters far less than the underlying documentation capability.
Use threat-aware habits: avoid suspicious redirects, be cautious with unknown downloads, and rely on browser privacy and security features. If a site behaves deceptively or requests unusual permissions, treat it as a risk.
Yes. Rules around age verification, content liability, and platform duties vary by jurisdiction. Even when general principles overlap, implementation details (and enforcement intensity) can differ.
Because abuse and policy violations can scale quickly. Automated systems help triage content and detect known patterns, while human review handles edge cases and higher-impact disputes.
In many jurisdictions, adult content can be legal if it meets access restrictions (especially age controls) and follows content-law requirements. Compliance focuses on reducing harm and meeting legal obligations, not on eliminating all adult material.
Yes, if the discussion is informational and objective—such as analyzing compliance, moderation, and platform responsibility. The key is avoiding sensationalism and focusing on risk controls and ethical standards.
The “P0rn0” keyword often appears in search because it’s associated with adult-content discovery. Yet the very consequential story is how platforms and suppliers manage responsibility: age assurance, moderation, rights documentation, security, and transparent user protections. In this domain, operational process quality is what ultimately determines whether a service can function responsibly at scale.
Note: This article intentionally avoids explicit content and does not provide instructions for bypassing safeguards. If you want, tell me the specific country or region you care about and whether your goal is research, policy drafting, or vendor evaluation—then I can tailor the conditions/requirements section accordingly.



This guide explains how to evaluate “1333” in a responsible, decision-ready way—covering quality signals, supplier verification, pricing considerations, and practical procurement checks. Background context discusses what “1333” typically refers to in catalog-based sourcing, why documentation matters, and how to reduce risk when selecting near products for ongoing operations.
This guide explains how 1333 influences sourcing and pricing decisions, with a professional lens on supplier selection, quality checks, and risk control. Background-wise, 1333 often appears as a reference code in procurement workflows, while pricing depends on specifications, lead times, and compliance requirements. Use the checklist and comparison elements to make defensible decisions.
This guide helps you evaluate dental care options by focusing on key decision factors like clinical suitability, supplier transparency, and pricing logic. Objectively, “Pacote” and related dental service terminology typically refer to bundled treatments or coordinated care plans. “Scheila Correia Silva” is presented here as an identified name within the topic context, without assuming additional claims.
This guide explains how Oraljob supports professional oral care planning and service coordination through role-ready workflows and transparent provider selection. It reviews what “Oraljob” typically refers to in oral-care service ecosystems, why structured onboarding matters, and how clinics and patients can evaluate suppliers responsibly using practical, industry-informed criteria.
Oraljob can help you understand how oral care services are structured, sourced, and scheduled for reliable outcomes. This guide reviews what “Oraljob” typically means in the dental services context, how suppliers and pricing models differ, and what to verify before booking. It also includes a comparison table, step-by-step checklist, and conditions for choosing dependable providers.
Pono is a concept used to describe a balanced, right, and life-guiding approach in daily practice. This guide explains the background of pono as it appears across cultural teachings, clarifies how people apply it in communication and decision-making, and offers objective considerations for responsible use, consistency, and reflection.
This guide explains what “Hjy” typically signals in procurement workflows and how to approach sourcing terms, price considerations, and supplier qualification with objective rigor. Background context covers how industry teams interpret ambiguous codes, document requirements, and evaluate cost drivers across supply chains, supporting better decisions without relying on unverified claims.
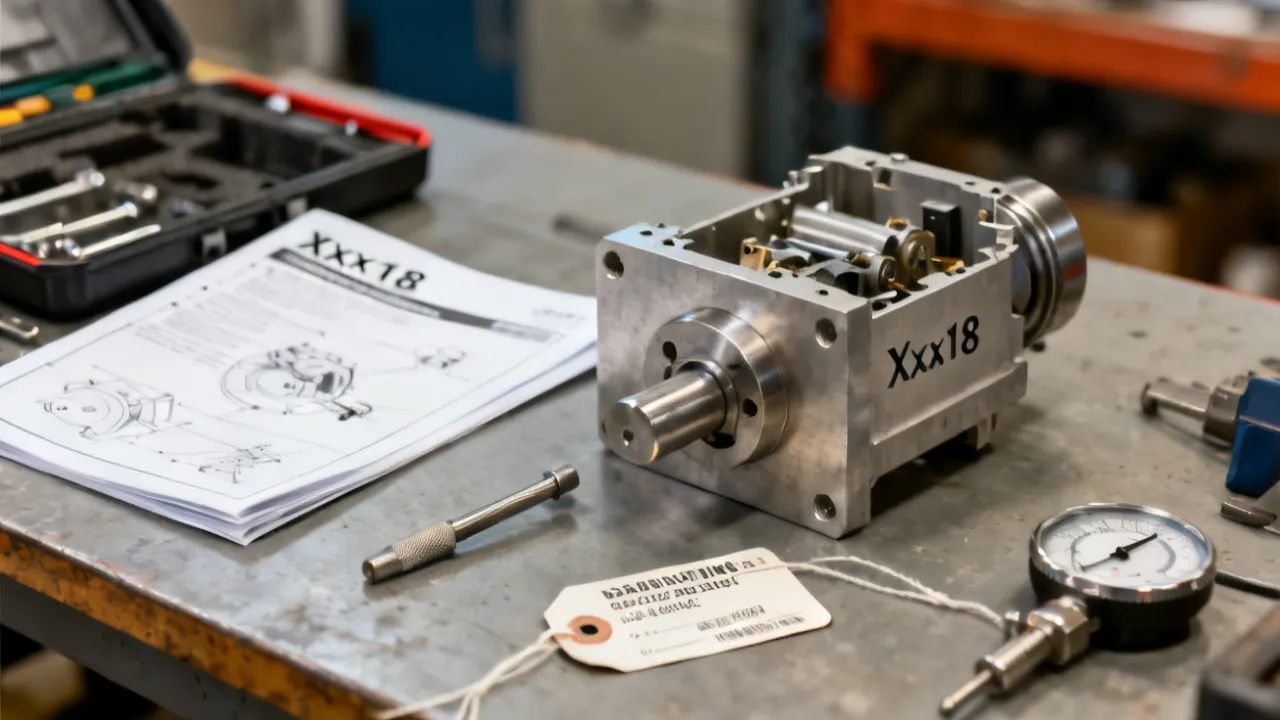
This guide explains how to evaluate Xxx18 specifications, suppliers, and procurement readiness. Objectively, Xxx18 is treated as a technical identifier used in product documentation and sourcing workflows, often tied to versioning, compatibility, and traceability. You’ll also find a practical decision framework, clear conditions for purchasing, and expert-style FAQs to reduce risk during selection.